Data sovereignty

You keep all right, title and interest in your data.

Affectli holds the live record of operations that cannot afford to fail. Data sovereignty means that record stays yours: you own your data by contract, choose where Affectli runs and decide who sees what, down to the column.

Data ownershipYours, by contract
Licensed asSaaS · PaaS · on-premises
Access policyDown to the column
Ownership

Data ownership, written into the contract.

Clause 8.1 of the Affectli Terms of Service keeps all right, title and interest in your data with you.

The same Terms set out how Affectli is licensed, where it runs and which law applies. They also set out the licence that Mi-C3, the company behind Affectli, needs to provide the service. Your legal team can review them in full before you sign.

Affectli Terms of ServiceSummary
Clause 8.1 · Your data

You retain all right, title and interest in its data.

Licensing · cl. 1.1, 2.4
Software as a service, platform as a service or on-premises.
On-premises · cl. 2.4
The software runs within your internal network, at your business location.
Governing law · cl. 14.1
Maltese law, with disputes referred to the Malta Arbitration Centre.
A summary for orientation. The full terms govern.Read the full terms ↗
Data separation

Each organisation’s data and configuration are kept separate.

Separation starts at the edge of your environment and continues inside it. Teams and workspaces group people by department, site or programme, each with its own permissions.

Vendors, contractors and partners work in the same platform as third-party users, limited to the work they are there to do.

Access control

Access by classification and role, down to the column.

Security policies are managed in one place. Each policy combines classification and role: what the data is, and who is asking. Policies apply in real time.

With the same rules, agencies, operators and contractors can share a common operating picture, each seeing only what its role allows.

Public safety and government at Mi-C3 ↗
Permissions · Harbour operations › Berths Classification · InternalPolicy live
Roles & teams
Port control 14
Marine services 22
Terminal security 9
Auditors 2
Third parties
Vendor V-07 · cranes 4
Contractor C-21 11
Partner · terminal 36
Levels
Database
Table
Column
Object · fieldPort controlMarineVendor V-07PartnerAuditor
Berth · scheduleEditViewViewViewView
Vessel call · ETA, berthEditEditDeniedViewView
Vessel call · cargo manifestViewDeniedDeniedOwn callsView
Vessel call · dangerous goodsViewViewOwn berthsViewView
Crane · telemetryViewDeniedContractedDeniedView
Crane · remote stopAct · approvalDeniedDeniedDeniedDenied
Gate access · person IDViewDeniedDeniedDeniedView
CCTV · Berth 7 camerasViewViewDeniedDeniedDenied
Effective access
Vendor V-07
Third party · crane maintenance
WorkspaceMarine services
Objects visibleSTS-03 · STS-04
TelemetryRead only
CommandsDenied
TicketsAssigned to V-07
Personal dataHidden
MessagingTicket threads
Applied in real timeClassification · role · column
Edit / actViewScoped to own objectsDenied
Classification-based

Rules that follow the data

Policies attach to classifications set in the Classifications Manager, so every object inherits the rules of the class it belongs to.

Role-based

Rules that follow the person

Roles, teams and workspaces decide what each person can view, edit and act on, including third-party users.

Down to the column

One record, different views

Policies apply in real time to databases, tables and columns, so the same record can show different fields to different people.

Encryption & messaging

End-to-end encrypted messaging, held in context.

Instant messages and broadcasts are end-to-end encrypted, so the conversation about an incident stays with the people working on it. In A-Box, each thread sits on the ticket, asset or incident it concerns, beside the tasks and documents that go with it.

  • End-to-end encrypted instant messaging, one-to-one and group
  • Broadcast messages, sent now or scheduled
  • Threads held on the object they concern

How data is protected in transit and at rest for your deployment model is set out in the security pack.

A-Box · INC-0389 End-to-end encrypted
Crane STS-04 · hydraulic pressure alarm · Berth 7
Port control07:12

STS-04 stopped at Berth 7 on a hydraulic pressure alarm. Oil on the quay apron. Vessel operations paused.

Vendor V-07Third party07:14

Technician on the way, ETA 20 min. We need entry through Gate 3.

07:15Terminal security

Gate 3 entry approved for V-07, 07:30 to 11:30. Badge check on arrival.

Broadcast · all berth teams · 07:16Berth 7 apron closed to vehicles until further notice.
On this incident
AssetSTS-04 · crane
LocationBerth 7
SeverityMedium
TaskWO-20944 · V-07
Documents3
Participants
Port controlOwner
Terminal securityMember
Vendor V-07Third party
Message INC-0389Encrypted
Deployment

SaaS, PaaS or on-premises. Your choice.

Affectli is licensed as software as a service, platform as a service or on-premises. It can run as a hosted service or on infrastructure the operator or authority controls. Choose the model that fits your security policy and your sector’s rules.

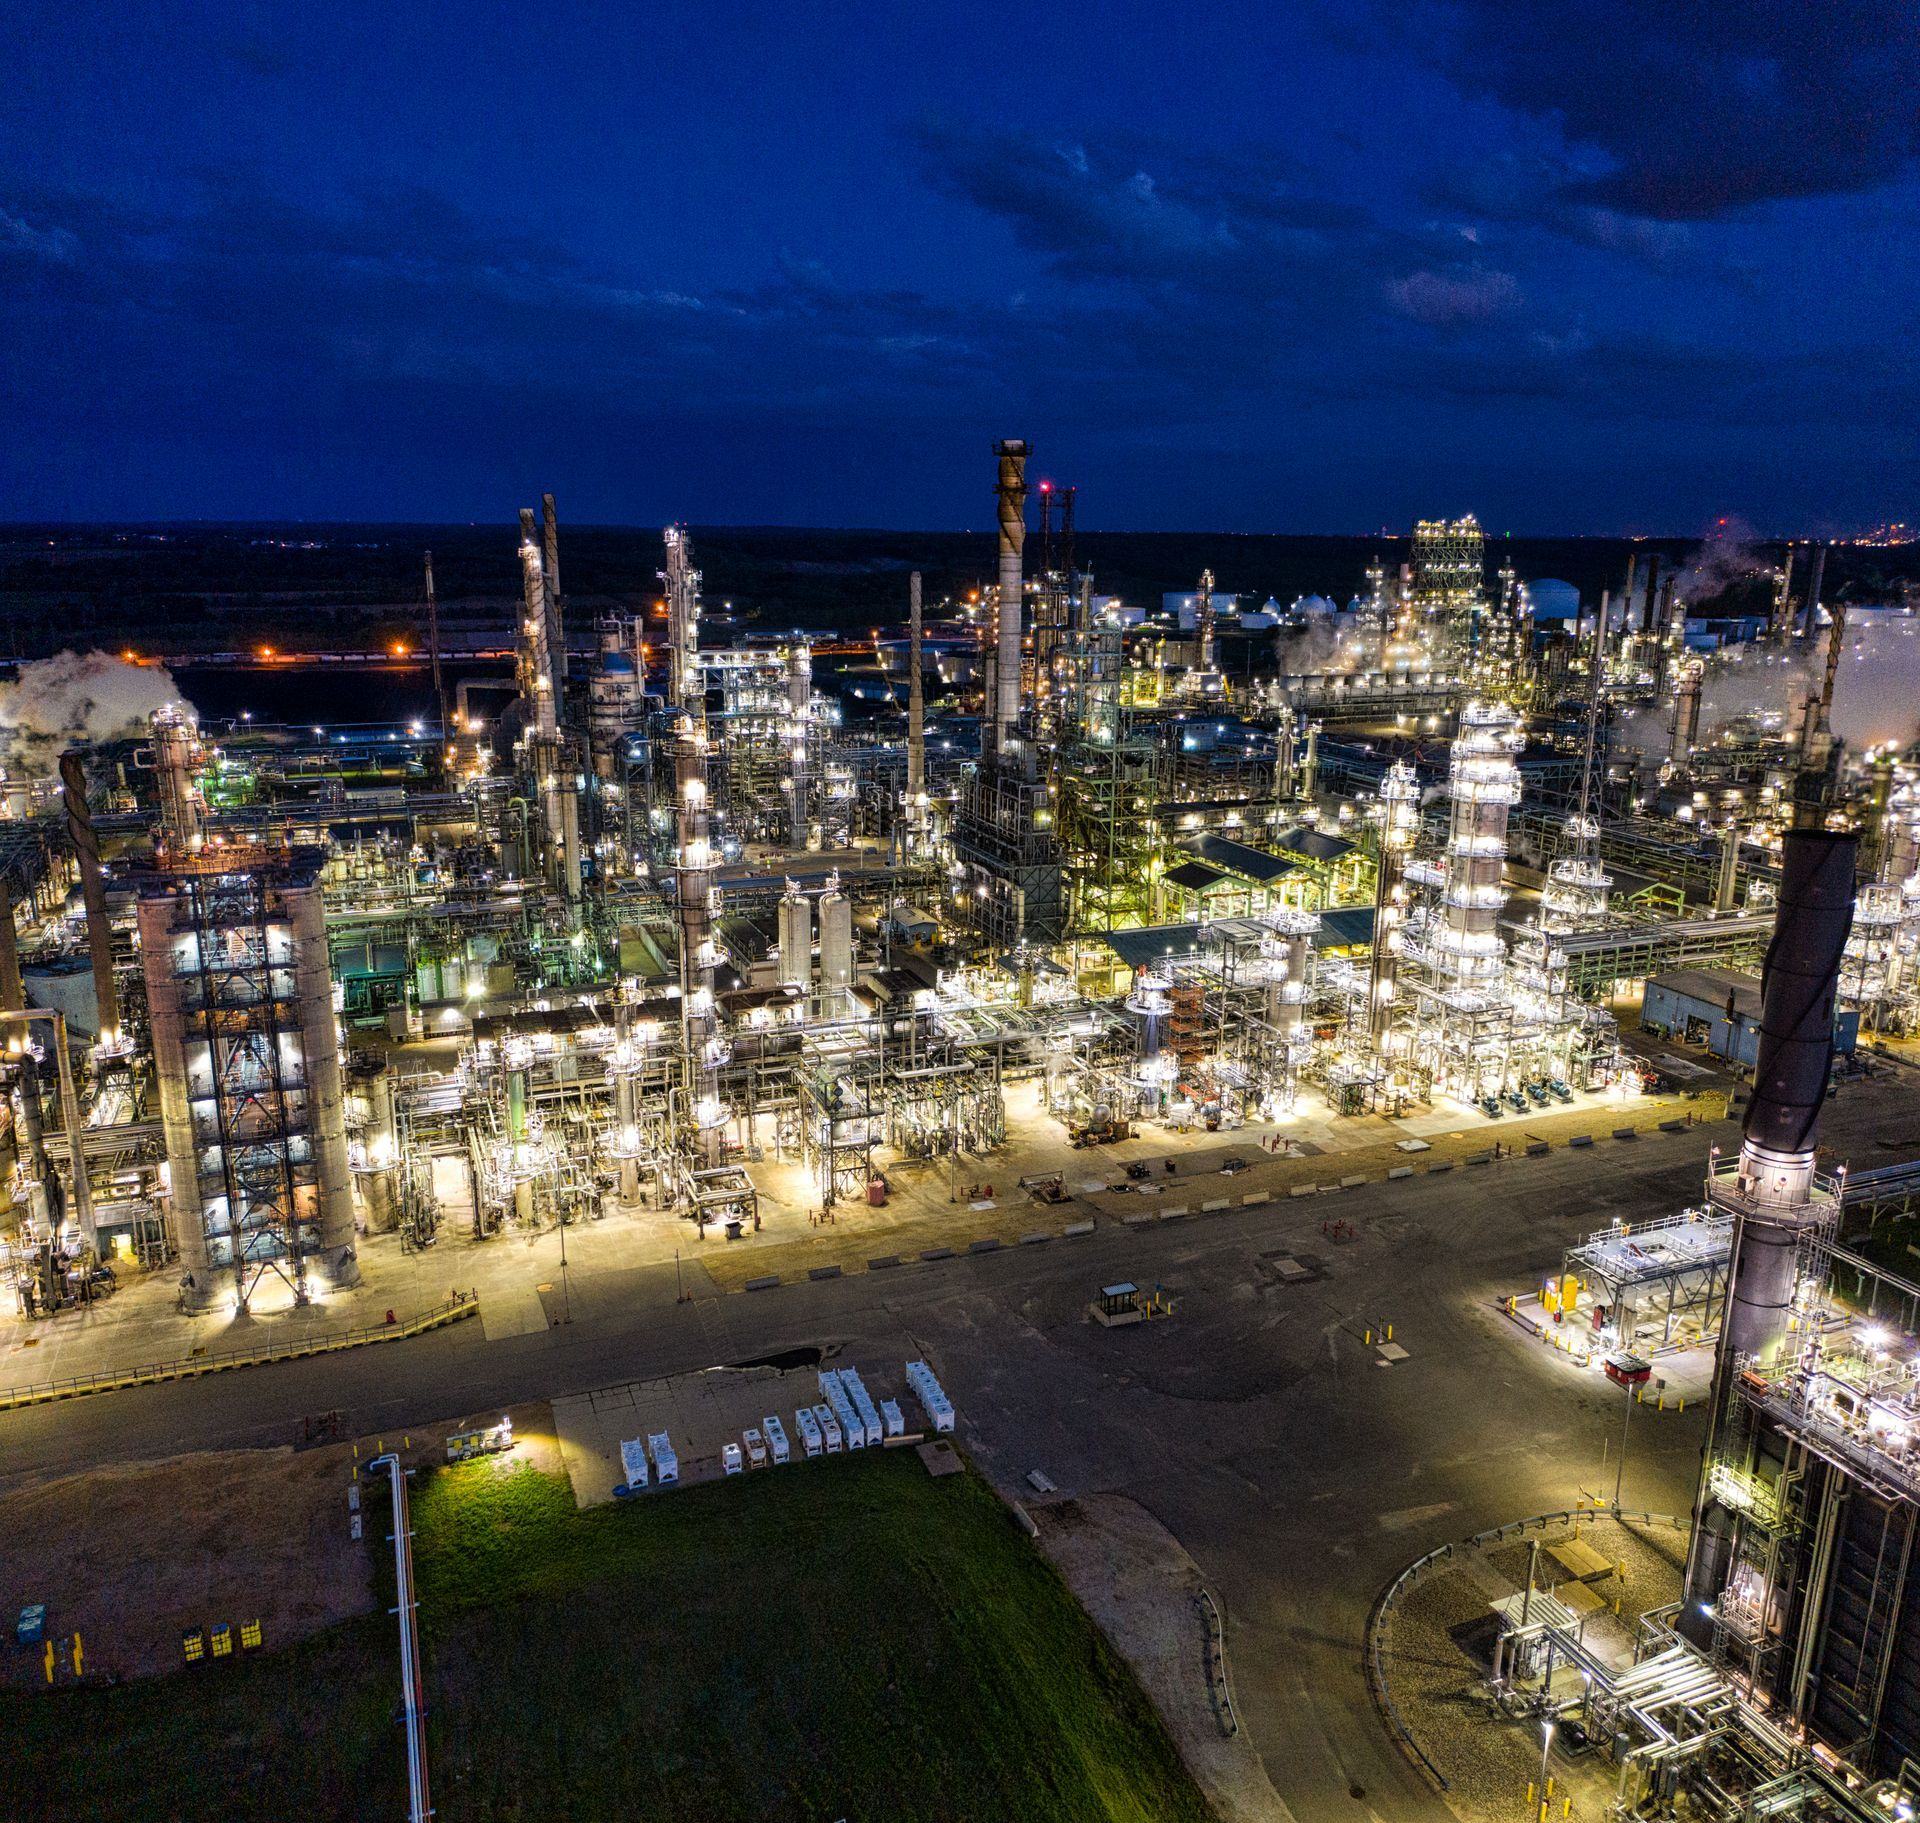
A refinery complex lit up at night, seen from above On-premisesYour network · your location
SaaS

Software as a service

Affectli delivered as a hosted service. Your teams sign in and work; the platform is run for you.
PaaS

Platform as a service

Affectli delivered as a platform, for organisations and channel partners that build and run their own applications in Affectli Designer.

On-premises

On your premises

The software runs within your own internal network, at your own business location, beside the systems it connects to.

Licensing models as set out in the Affectli Terms of Service, cl. 1.1 and 2.4

Certifications

Independent assurance, held by Mi-C3.

Mi-C3 holds ISO/IEC 27001, ISO 9001, ISO/IEC 20000-1 and ISO 14001 certification at company level. Scope and detail are on the Mi-C3 Trust page.

View certifications at Mi-C3 ↗

Certificates held by Mi-C3 International Limited

Open-source foundations

Built on open, widely supported software.

Mi-C3 rebuilt Affectli on open-source software after starting on a proprietary database. Big-data governance runs on open-source technologies, and the core components are widely used and independently supported.

PostgreSQLRelational database
Apache DruidReal-time analytics
ActivitiBPMN 2.0 workflow engine
ReactUser interface
GraphQLAPI layer
Apache SparkLarge-scale data processing
Database support

Percona provides support and consulting for the PostgreSQL databases behind Affectli, under an agreement announced in April 2021.

FAQ

Questions on data sovereignty and security.

Short answers to the questions that come up in every security and architecture review. Company-level governance and certification scope sit with Mi-C3.

Data sovereignty for critical infrastructure at Mi-C3 ↗
Who owns the data we put into Affectli?
You do. Under the Affectli Terms of Service, you retain all right, title and interest in your data (clause 8.1). The Terms also set out the licence Mi-C3 needs to provide the service. Your legal team can review them in full before you sign.
Where can Affectli run?
Affectli is licensed as software as a service, platform as a service or on-premises. On-premises, the software runs within your own internal network at your own business location.
Can vendors and contractors use Affectli without seeing everything?
Yes. Teams and workspaces include third-party users such as vendors, contractors and partners. Their access is set by classification and role, down to individual columns, so a vendor can be limited to the assets it maintains.
Is our data kept separate from other organisations?
Yes. Each organisation’s data and configuration are kept separate. Within your environment, teams and workspaces control what each department and each third party can see and do.
How is data protected in transit and at rest?
Instant messages and broadcasts inside Affectli are end-to-end encrypted. The security pack sets out how data is protected in transit and at rest for the deployment model you choose.
Which certifications does Mi-C3 hold?
Mi-C3, the company behind Affectli, holds ISO/IEC 27001 (information security management), ISO 9001 (quality management), ISO/IEC 20000-1 (IT service management) and ISO 14001 (environmental management). Scope and detail are on the Mi-C3 Trust page ↗.
What is Affectli built on?
Open-source foundations, including PostgreSQL, Apache Druid, Activiti for BPMN 2.0 workflows, React, GraphQL and Apache Spark. Percona provides support and consulting for the PostgreSQL databases behind Affectli.
How does Affectli relate to NIS2?
The NIS2 Directive (EU) 2022/2555 sets minimum cybersecurity risk-management measures in Article 21(2), including access control, encryption and asset management. Affectli supports those measures with access by classification and role, end-to-end encrypted messaging and a live register of assets in the ontology. Meeting the obligations remains the responsibility of each entity. NIS2 obligations for operators at Mi-C3 ↗
Which law governs the contract?
Client contracts are governed by Maltese law, with disputes referred to the Malta Arbitration Centre (clause 14.1 of the Terms of Service).
Next step

Review Affectli with your security team.

Bring your security and architecture questions to a demo. A product specialist will walk through ownership, data separation, access control and deployment against your requirements.